

Mulesoft Anypoint Platform SSO Implementation (Auth0)
Mulesoft Anypoint platform SSO configuration. Log in through Social media, Database, Active directory or Auth0 user, etc.
Identity Management: Anypoint Platform
You can configure identity management in the Anypoint Platform to set up users for single sign-on (SSO). There are two ways to configure identity management using one of the following single sign-on standards:
OpenID Connect: End-user identity verification by an authorization server including SSO
SAML 2.0: Web-based authorization including cross-domain SSO
Here we can use OpenID Connect to connect IDP provider(Auth0). Through Auth0 we can log in to Anypoint platform using user created in Auth0, simple database, Active Directory, or any social media like Google, Facebook, and Linkedin, etc.
End of this exercise you will be able to login to the Anypoint platform using the Auth0 credential and Gmail account.
Identity Management Process
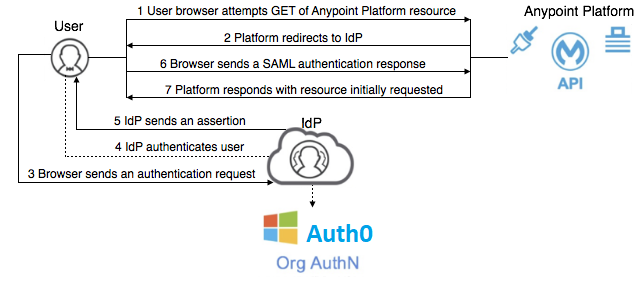
Identity Provider (Auth0)
An identity provider is a system entity that creates, maintains, and manages identity information for principals. It offers user authentication as a service. Relying party applications, such as web applications, outsource the user authentication step to a trusted identity provider.
Auth0 is a flexible, drop-in solution to add authentication and authorization services to your applications. You can connect any application (written in any language or on any stack) to Auth0 and define the identity providers that you want to use (how do you want your users to log in to the system)to log in.
Identity Provider Configuration
- Login into the Anypoint platform and click on access manager
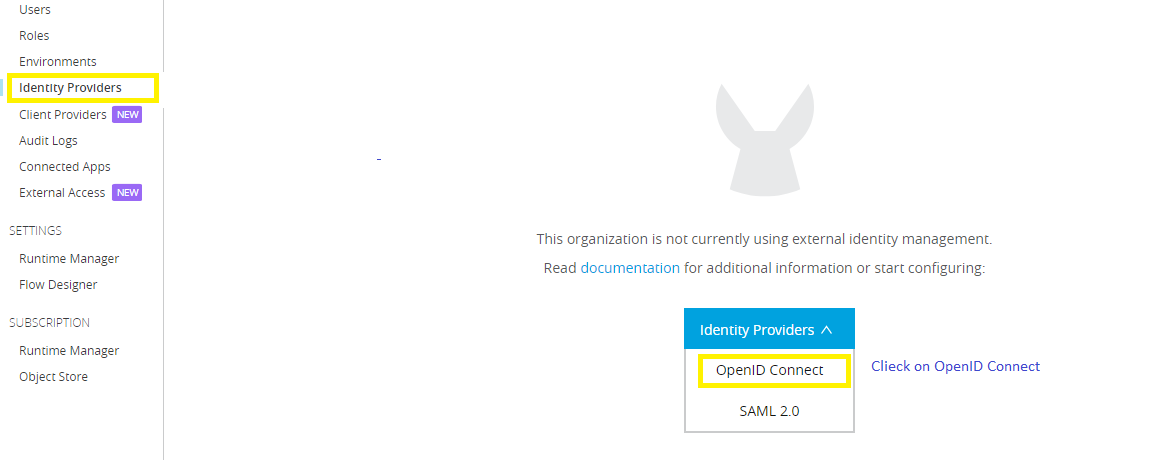
- Click Identity provide from Access management
- Click Identity Providers
- Click Identity Providers and select OpenID connect
- Click Ok
Copy redirect URI from Identity Client Registration
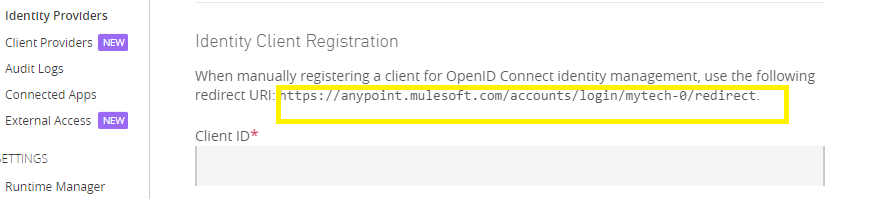
e.g. : https://anypoint.mulesoft.com/accounts/login/mytech-0/redirect
Note mytech-0 is Organization domain above URL will be configured in Auth0 as Callback URLs.
Create Application in Auth0
Create new application SSO-Mule then select Machine to Machine applications and click Create
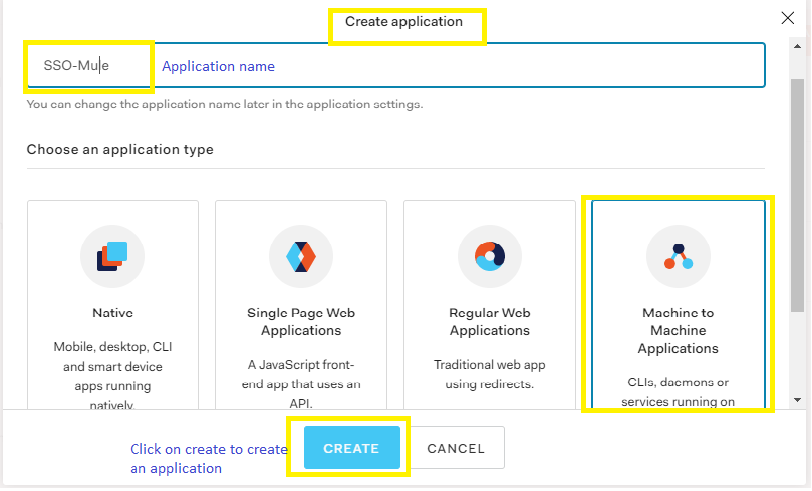
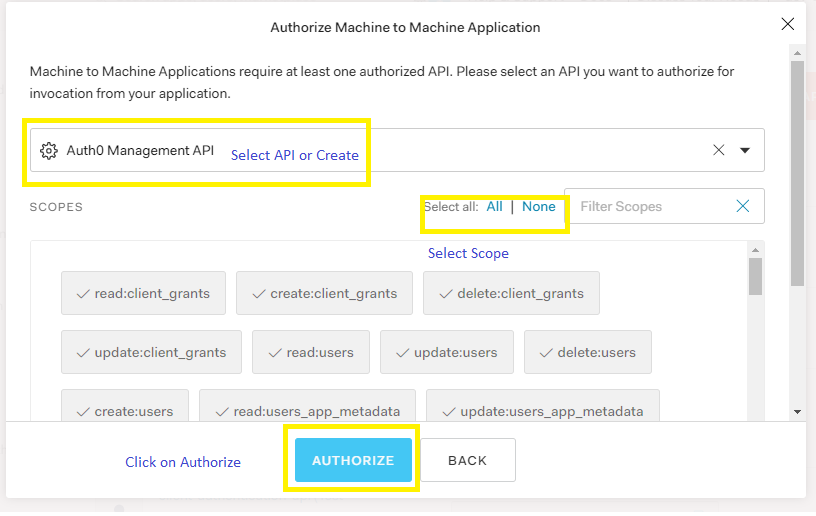
Select API from the drop (you can select default if not created new )and scope and click Authorize
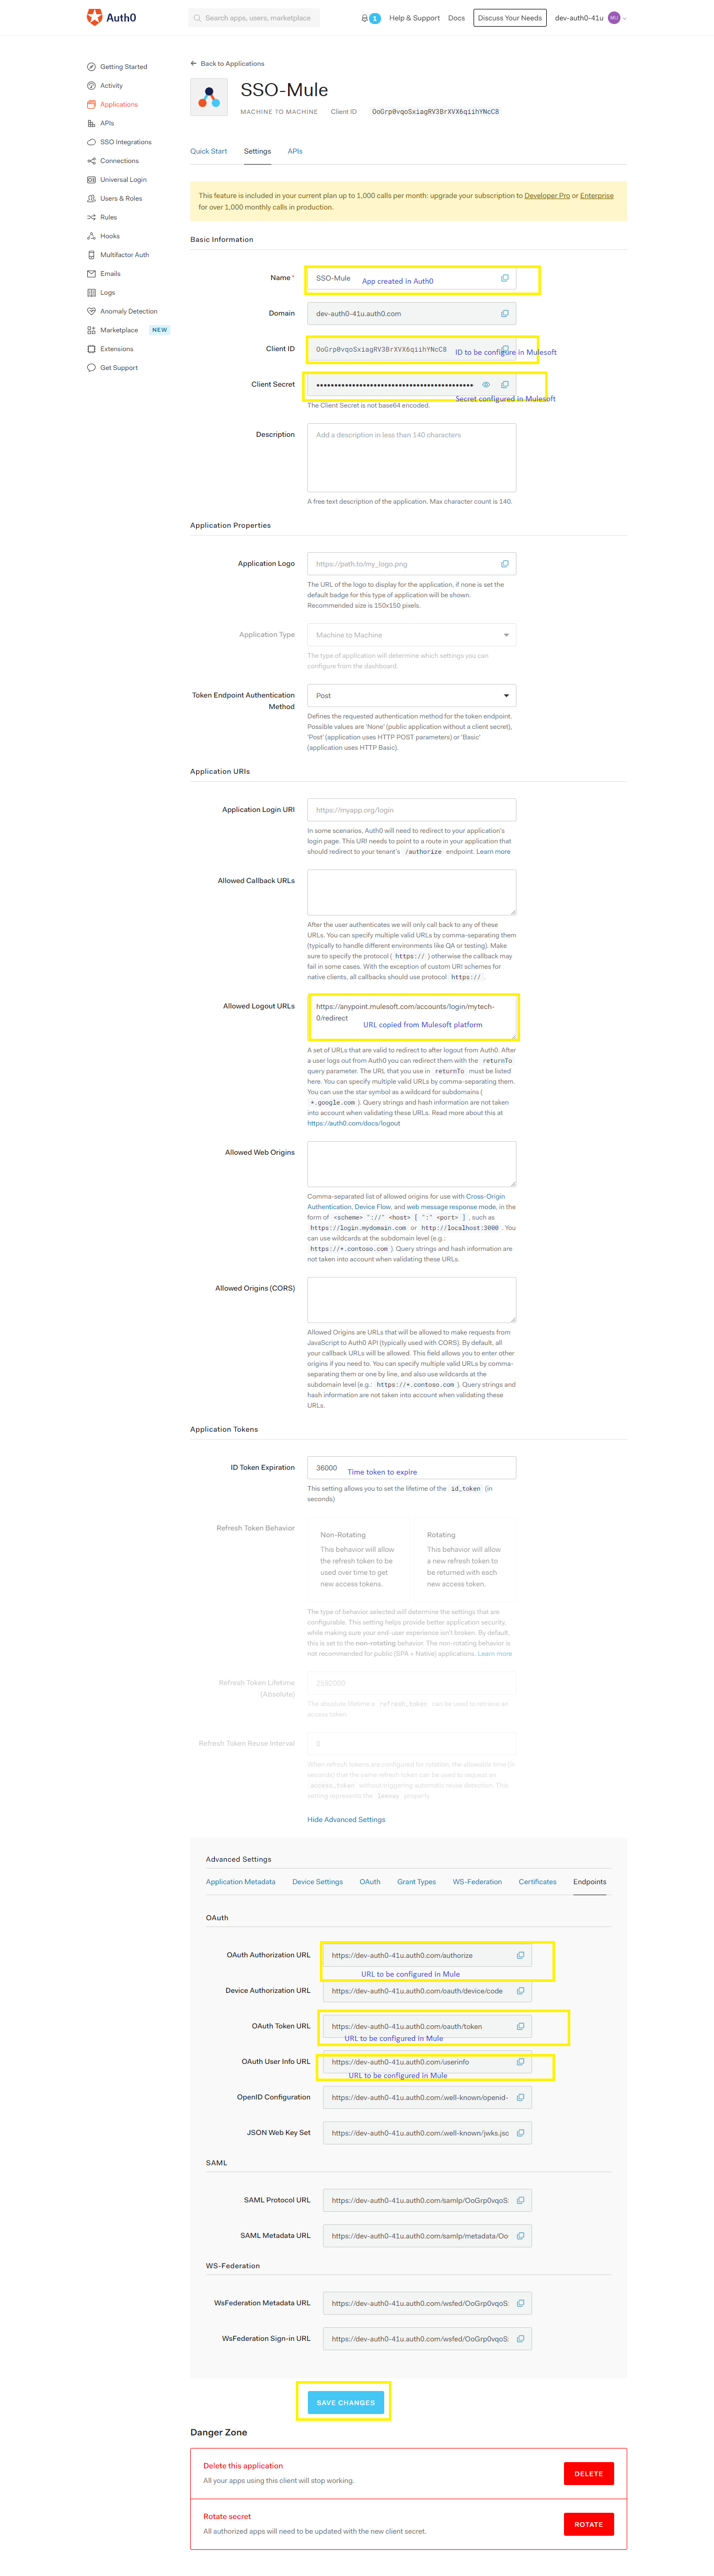
Select created application and update the details
Add login URL: This URI needs to point to a route in your application that should redirect to your tenant’s
Add Logout URL: A set of URLs that are valid to redirect to after logout from Auth0
Add callback URL: After the user authenticates that will only call back to these URLs
Note: https://anypoint.mulesoft.com/accounts/login/<organization doain>/redirect) received from previous steps
Click show Advanced settings > Grant Types: check Authorization Code
Click save changes
Copy Client ID, Client Secret, OAuth Authorization URL, and OAuth Token URL to configure Identity Providers in the Anypoint platform
Configure all attributes as per copied in previous steps or configured in Auth0.
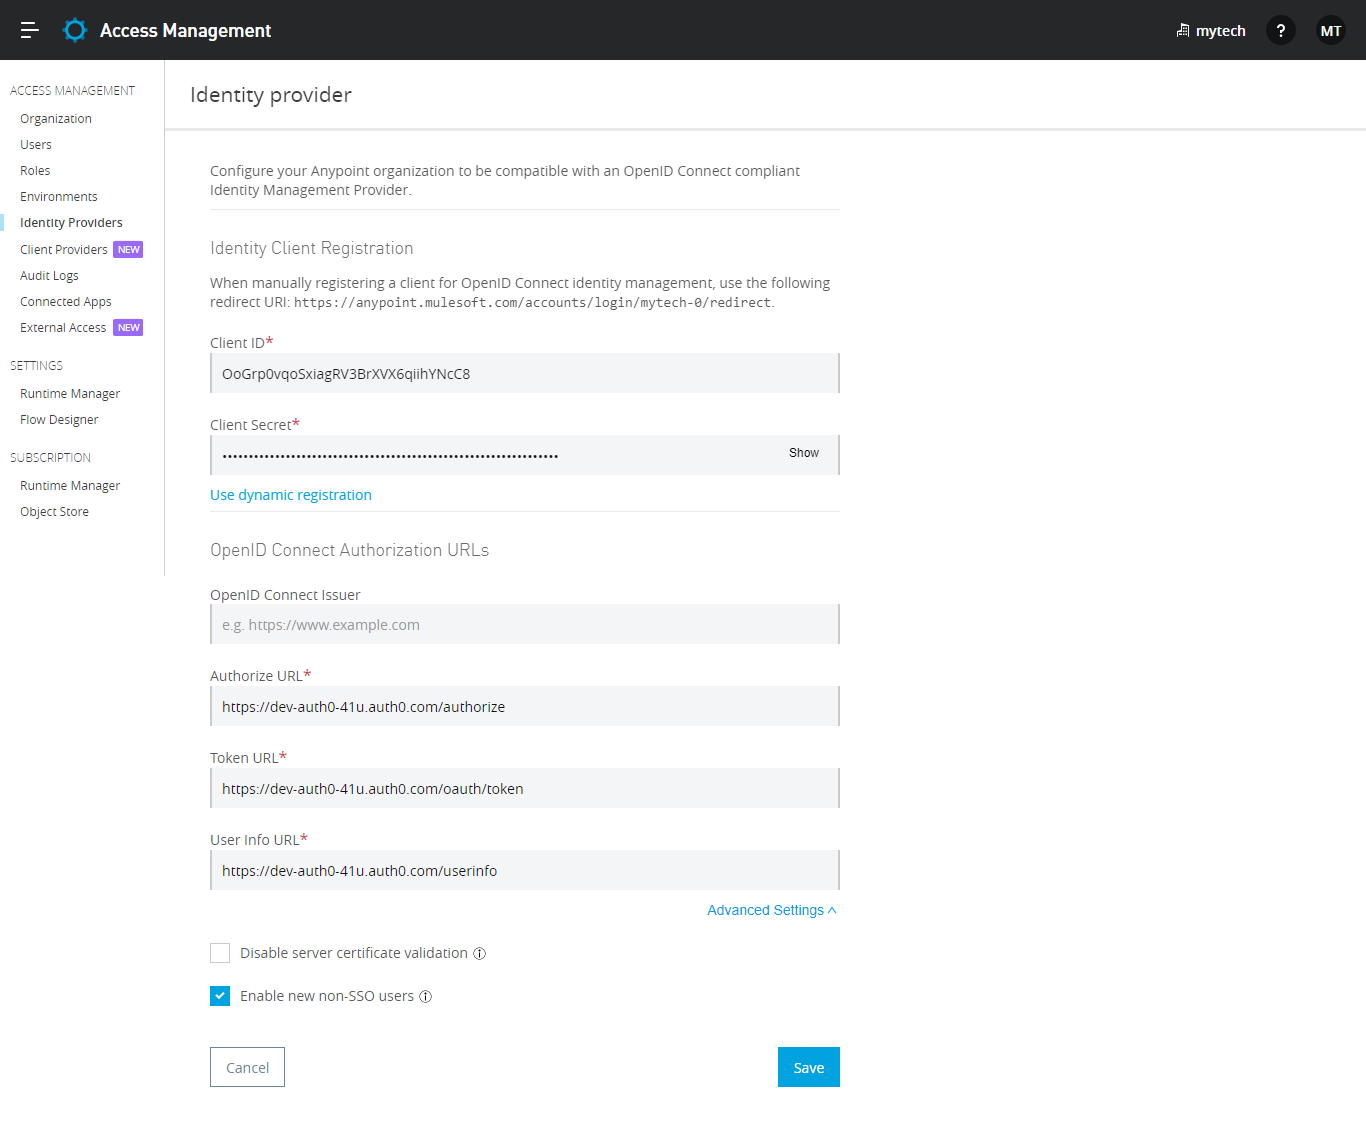
Click Save.
Create a Connection in Auth0 against that user get validated.
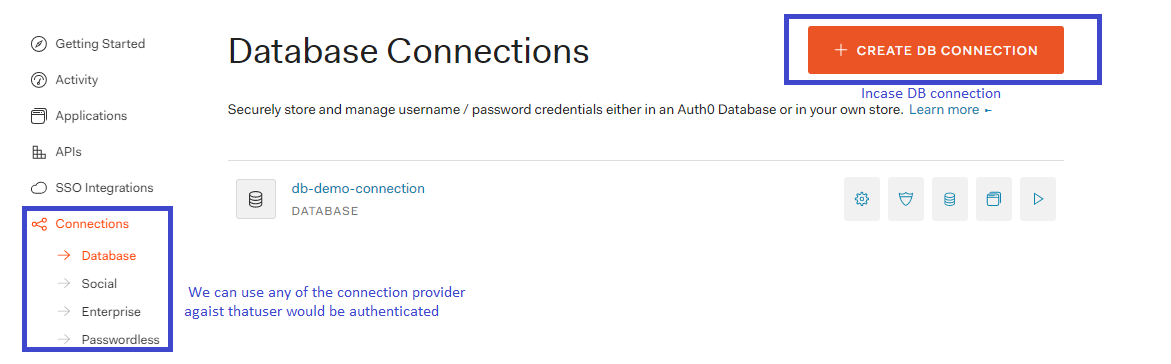 Test SSO
Click login URL: https://anypoint.mulesoft.com/accounts/login/mytech-0/
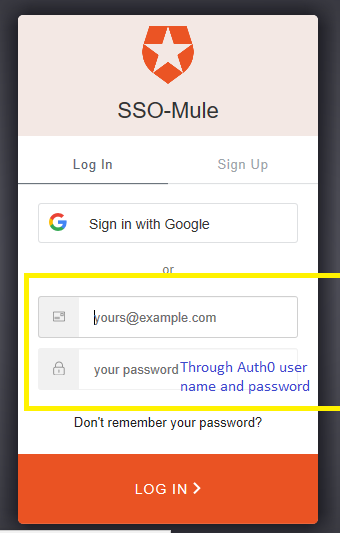
or
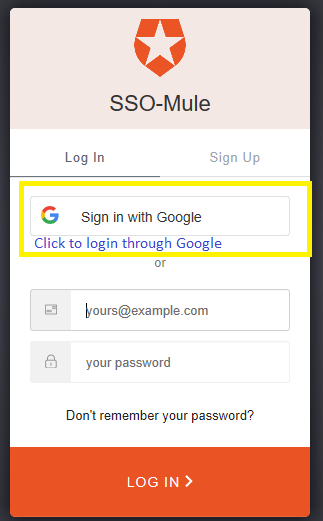
Provide user name and password created in AuthO or click on Sign In with Google.
After successful login, you will be redirected to the Anypoint platform page.
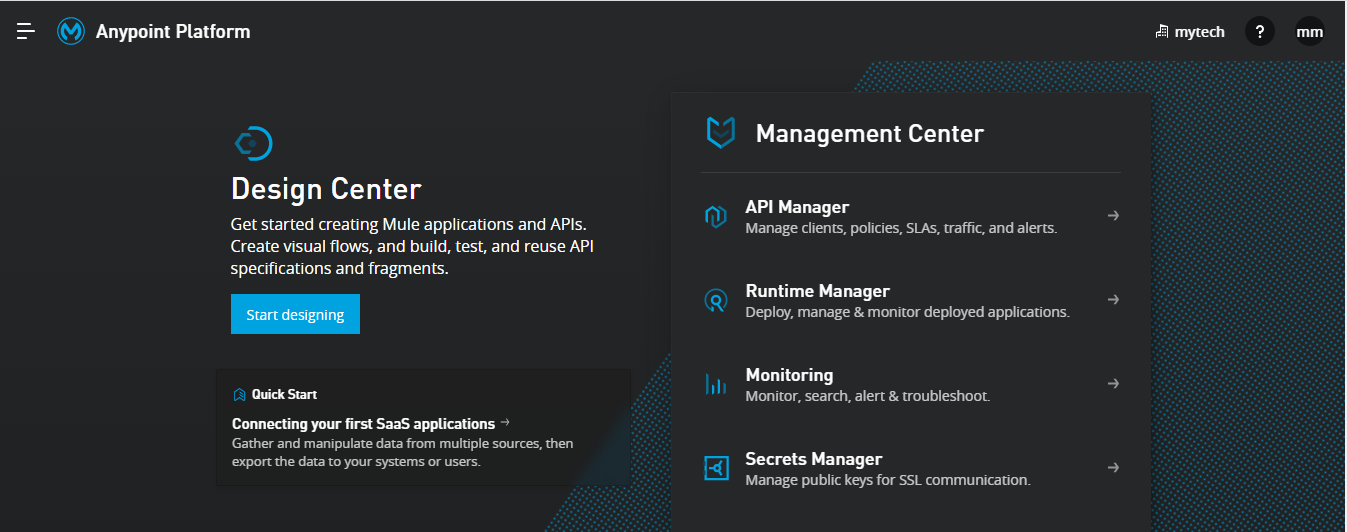
Note: Group and Role you can manage through mapping Role management IDP and Anypoint platform.
Opinions expressed by DZone contributors are their own.