

How Does HTTP Basic Authentication Work in Spring Security?
Want to learn more about how to HTTP basic authentication works in Spring Security? Check out this post to learn more about HTTP basic authentication.
In this article, we will attempt to understand exactly how HTTP basic authentication works in Spring Security. If you remember, when you use HTTP basic for authentication purposes, the client, e.g. your browser or a REST client, sends login credentials in the HTTP request header.
The header is aptly named as "Authorization," and it contains Base64-encoded string, which is created by concatenating the username and password using a colon.
For example, if the username is "johnsmith" and the password is "JOHN3214," then they will be concatenated as"johnsmith:JOHN3214" before encoded using Base64 encoding algorithms.
The server, when it receives such a request, it extracts the value of the "Authorization" header and decodes the content of this header using the same algorithm Base64 for authenticating the user.
In a previous post, we used <http-basic>l; in the XML configuration or the httpBasic() method on the HttpSecurity object to enable basic authentication.
Now, let's see exactly how Spring Security supports HTTP basic authentication and how things move inside the Spring Security space when it receives a login request and HTTP basic authentication is enabled at the server end.
How Spring Security Processes HTTP Basic Authentication Requests
When you use the <http-basic>l; configuration element, Spring Security's BasicAuthenticationFitler comes into the picture, which basically checks to see if the incoming HTTP request contains the "Authorization" header or not and its value starts with "Basic."
A BasicAuthenticationEntryPoint strategy is also configured into the ExceptionTranslationFilter on startup, which is required to handle requests that do not contain the "Authorization" header.
When you make an HTTP request to a protected URL, e.g. /admin/users from the browser without adding the "Authorization" header, then Spring Security throws an access-denied exception that is handled by the ExceptionTranslationFilter .
This filter then delegates to a particular implementation strategy of the AuthenticationEntryPoint interface, which is the BasicAuthenticationEntryPoint in our case.
This class adds the header "WWW-Authenticate: Basic real="Spring Security Application" to the response and then sends an HTTP status code of 401 (Unauthorized) to the client, e.g. to your browser, which knows how to handle this code and work accordingly. Because of this, it shows a dialog box prompting for username and password, as shown below:
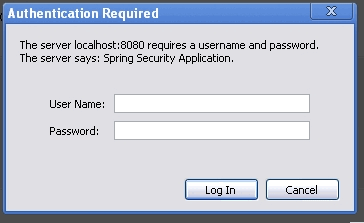
When you put the username and password and submit the request, the request again follows the filter chain until it reaches the BasicAuthenticationFilter.
This filter checks the request headers and the location for the Authorization header, starting with "Basic." It will look something like this: Authorization: Basic CDWhZGRpbjpvcGVuc2AzYW1l .
The BasicAuthentictionFilter then extracts the content of the Authorization header and uses the Base64 algorithm to decode the login credentials to extract the username and password from the decoded string.
Once it has that information, the filter creates a UsernamePasswordAuthenticationToken object and sends it to the authentication manager for authentication in the standard way.
The authentication manager will ask the authentication provider ( in memory, JDBC backed or LDAP based) to retrieve the user and then create an Authentication object with it. This process is standard and independent of using HTTP basic for authentication and is applicable for digest authentication, as well.
If you are working in RESTful web services, you can also use the curl command to send the HTTP request with the Authorization error for HTTP basic authentication. I have found curl to be an easy way to test web services by sending various HTTP command from the command line.
You can also see my post on how to test RESTful web services to check out some practical examples of curl, like sending post requests, a request with HTTP basic and digest authentication, etc.
As I have said before, basic authentication is not secure. Anyone who can intercept the request can decode the password, hence it is only used for testing purposes, while more sophisticated digest authentication and OAuth is used in the real-world application, particularly if you are want to secure your REST API.

That's all about how HTTP basic authentication works inside Spring Security. You have seen the full workflow of what happens when an HTTP request hits a protected URL ,which requests basic authentication. Basically, the BasicAuthenticationFilter does most of the job along withBasicAuthenticationEntryPoint.
Published at DZone with permission of Javin Paul. See the original article here.
Opinions expressed by DZone contributors are their own.