

Secure .NET Core Applications From ClickJacking: .NET Core Security Part III
We continue our look at .NET Core security by examining ClickJacking and how to prevent this type of cyberattack in your web app.
In these series of posts, we will go over how to secure your .NET Core applications.
In this post, we will look at how to secure your .NET Core application from a ClickJacking attack.
What Is ClickJacking?
Per OWASP:
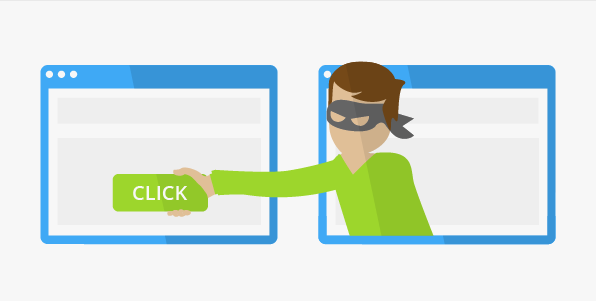
"Clickjacking, also known as a ' UI redress attack,' is when an attacker uses multiple transparent or opaque layers to trick a user into clicking on a button or link on another page when they were intending to click on the top level page. Thus, the attacker is ' hijacking' clicks meant for their page and routing them to another page, most likely owned by another application, domain, or both."
For example:
- A malicious website invites the user to click a button by showing some ad.
- The user does not know that the malicious site might have put a Transfer Money button just behind the submit button in such a way that user cannot see the transfer button.
- The user’s authentication details are then readily available to the hackers. And, if the browser contains the user's authentication protocols to his/her bank account, then the attacker has access to that account.
- Additionally, the malicious site can pull the details of the user’s bank account by showing the bank’s site in a frame.
- When the user clicks on the button, the amount will be transferred from the user’s account to the hacker’s account.
How to Prevent This?
We need to prevent our site to open in a frame or we can allow our site to be opened in a frame only for same domain or any specific domain.
We can prevent this by adding some extra headers which are:
- X-FRAME-OPTIONS : DENY
This prevents the browser from showing this page in an iFrame:
- X-FRAME-OPTIONS : SAMEORIGIN
This allows frame in own domain:
- X-FRAME-OPTIONS : ALLOW-FROM https://mysite.com
This allows frame in any specific domain
How to Prevent This in .NET Core
In .NET Core, we can add these headers in the Configure method of Startup.cs class as below:
app.Use(async (context, next) =>
{
context.Response.Headers.Add("X-Frame-Options", "DENY"); // This
context.Response.Headers.Add("X-Frame-Options", "SAMEORIGIN"); // Or this
await next();
});
Or you can use the NWebSec Nuget package which allows you to do this in the middleware.
First, install the NWebSec Nuget package:

And then add below line in the Configure method of the Startup.cs class:
app.UseXfo(0 => o.Deny());Important Notes –
- If you are using the AntiForgery token in your application then this token by default sets X-Frame-Option with value SAMEORIGIN to prevent the site from ClickJacking.
- So if you are using AntiForgey along with the options I mentioned above then it may create some problems because, along with our changes for ClickJacking, the AntiForgeryToken also tries to set the headers.
- If you want to disable setting headers for frames in AntiForgeyToken then simply add the below line:
services.AddAntiforgery(o => o.SuppressXFrameOptionsHeader = true);This will disable that header in Antiforgery and we can handle the ClickJacking on our own. (Ref – https://github.com/aspnet/Mvc/issues/3958)
Hope this helps!
Published at DZone with permission of Neel Bhatt. See the original article here.
Opinions expressed by DZone contributors are their own.