

Some Image-Based Exploits With Their Prevention
We take a look at image-based exploits that are common to websites, in this case, those that are backed by PHP. We also look at what devs can do to prevent them.
Images can be used to run malicious scripts over the browser and can also be used to download Trojans if not handled carefully by your website. Too much trust on user input can cause damage to your clients.
In this post, we will run malicious scripts using a simple image viewer functionality and lastly we will discuss how we can resolve this.
Programming Language
HTML, PHP
Git Repository
https://github.com/csanuragjain/extra/tree/master/ImageExploit
Website
https://cooltrickshome.blogspot.in/2017/07/some-image-based-exploits-with-their.html
One of Image Vulnerability I reported:
https://hackerone.com/reports/221928
Scenario #1:
In this scenario, we will show how lacking Content-Type while displaying images can run malicious scripts.
Malicious Image

Description
1) Right Click on the above Image and then choose 'Save Image As.'
2) Name it as exifxss.jpg and save it.
3) Otherwise, you can also get it from the git location.
showImage.php
 <?php
 include('exifxss.jpg');
 ?>
Description
A simple PHP file showing the above .jpg file.
Output:
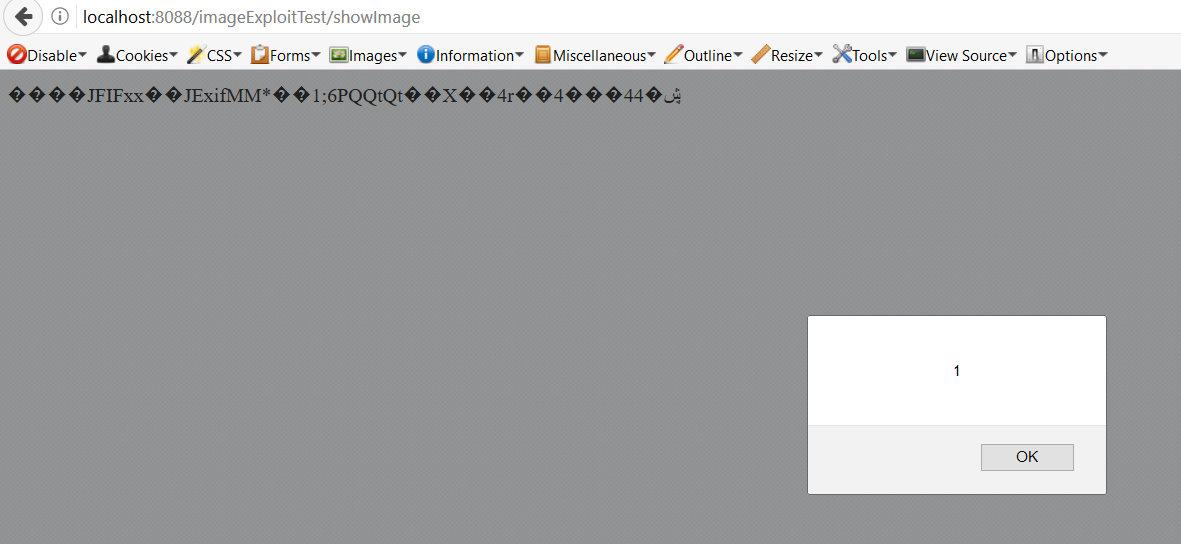
- When you access showImage.php on your browser, you will expect to see the image but instead, you will see several pop-ups coming up.
- This happens because the PHP page is not setting the Content-Type which makes PHP show the image as HTML. Since the image has several alert messages, they start popping up.
- showImage.php needs to make sure that it sets the correct Content-Type and also make sure that it does not set the user provided Content-Type.
Scenario #2:
In this scenario, we will show how a simple looking image when downloaded can become an exploit.
Caution: This will run notepad, calc, msconfig, services.msc on your computer, although it won't perform anything malicious.
Malicious Image

Description
1) Right Click on above Image and then choose 'Save Image As.'
2) Name it as exifxss.bat and Save it.
3) Otherwise, you can also get it from the git location.
showImage2.html
<img src="image.bat" width=500 height=500/>
Description
A simple HTML file showing the image image.bat.
Output:
- On accessing the above HTML, you would see the Bugs Bunny image (nothing suspicious).
- Now, right click on the image and save the image. It should be saved as image.bat.
- On opening it, the malicious payload gets executed, opening up notepad, services.msc, msconfig, and calc.
- To prevent it, make sure that users are never allowed to store any non-image extension file.
Please let me know your suggestions and comments.
Hope it helps!
Published at DZone with permission of Anurag Jain. See the original article here.
Opinions expressed by DZone contributors are their own.