
DZone
Thanks for visiting DZone today,
Edit Profile
  • Manage Email Subscriptions
  • How to Post to DZone
  • Article Submission Guidelines
Sign Out View Profile
  • Post an Article
  • Manage My Drafts
Newsletter
Log In / Join
Refcards Trend Reports
Events Video Library
Refcards
Trend Reports

Events

View Events Video Library

Related

  • Sharing SBOMs Securely Without Giving Too Much Away
  • Advanced Docker Security: From Supply Chain Transparency to Network Defense
  • How Migrating to Hardened Container Images Strengthens the Secure Software Development Lifecycle
  • Technical Deep Dive: Scaling GenAI-Enhanced SBOM Analysis from Trivy Fix to Enterprise DevSecOps

Trending

  • A Walk-Through of the DZone Article Editor
  • Build a Voice Assistant With Gemini Live API
  • How to Build Your Own AI SRE From Scratch
  • The Real Cost of Change in Software Development

Draft This article hasn't been published, so readers can't see it.

In moderation This article is waiting for review, so readers can't see it yet.

Deleted This article has been deleted, so readers can't see it.

  1. DZone
  2. Software Design and Architecture
  3. Security
  4. Software Security Treat or Threat? Leveraging SBOMs to Control Your Supply Chain Chaos [Infographic]

Software Security Treat or Threat? Leveraging SBOMs to Control Your Supply Chain Chaos [Infographic]

Learn about the required and recommended SBOM components — plus key security practices — to enhance your security posture along the entire software supply chain.

By 
DZone Editorial
·
Derrick Kean Auxtero
·
Aug. 13, 25 · Presentation
Post on X (opens in a new tab) Share on LinkedIn (opens in a new tab)
2.4K Views

Join the DZone community Save articles, join the discussion, and download Refcards and Trend Reports with a free account.

Join for free Already a member? Log in

Editor's Note: The following is an article written for and published in DZone's 2025 Trend Report, Software Supply Chain Security: Enhancing Trust and Resilience Across the Software Development Lifecycle.


Software supply chain security is on the rise as systems advance and hackers level up their tactics. Gone are the days of fragmented security checkpoints and analyzing small pieces of the larger software security puzzle. Now, software bills of materials (SBOMs) are becoming the required norm instead of an afterthought. So the question is: Are supply chains and SBOMs a sweet pairing or a sticky solution?

Below are your playing cards, featuring key data from DZone audience's responses to our Software Supply Chain Security survey, to help guide you along your journey. So dodge the sour code, unwrap the SBOM mystery flavors, and follow the sweet trail toward a strengthened security posture. 

SBOM Savories

  • 63% generate and use SBOMs in their development and security processes.
  • 53% use SBOM generation and validation as their primary strategy to minimize attack surfaces.
  • 51% update their SBOMs on a scheduled basis.

Sticky Vulnerabilities

  • 63% name inconsistent or duplicate security controls as their top challenge in complex toolchains.
  • 26% feel fully prepared to meet evolving regulatory compliance standards.
  • 47% cite container images as their top supply chain threat.

Sweet Dependencies

  • 63% note zero-trust architecture as the most critical strategy to secure hybrid or multi-cloud environments.
  • 61% say using AI/ML for threat detection led to better threat prioritization.
  • 68% use data masking or tokenization to protect data across CI/CD workflows.
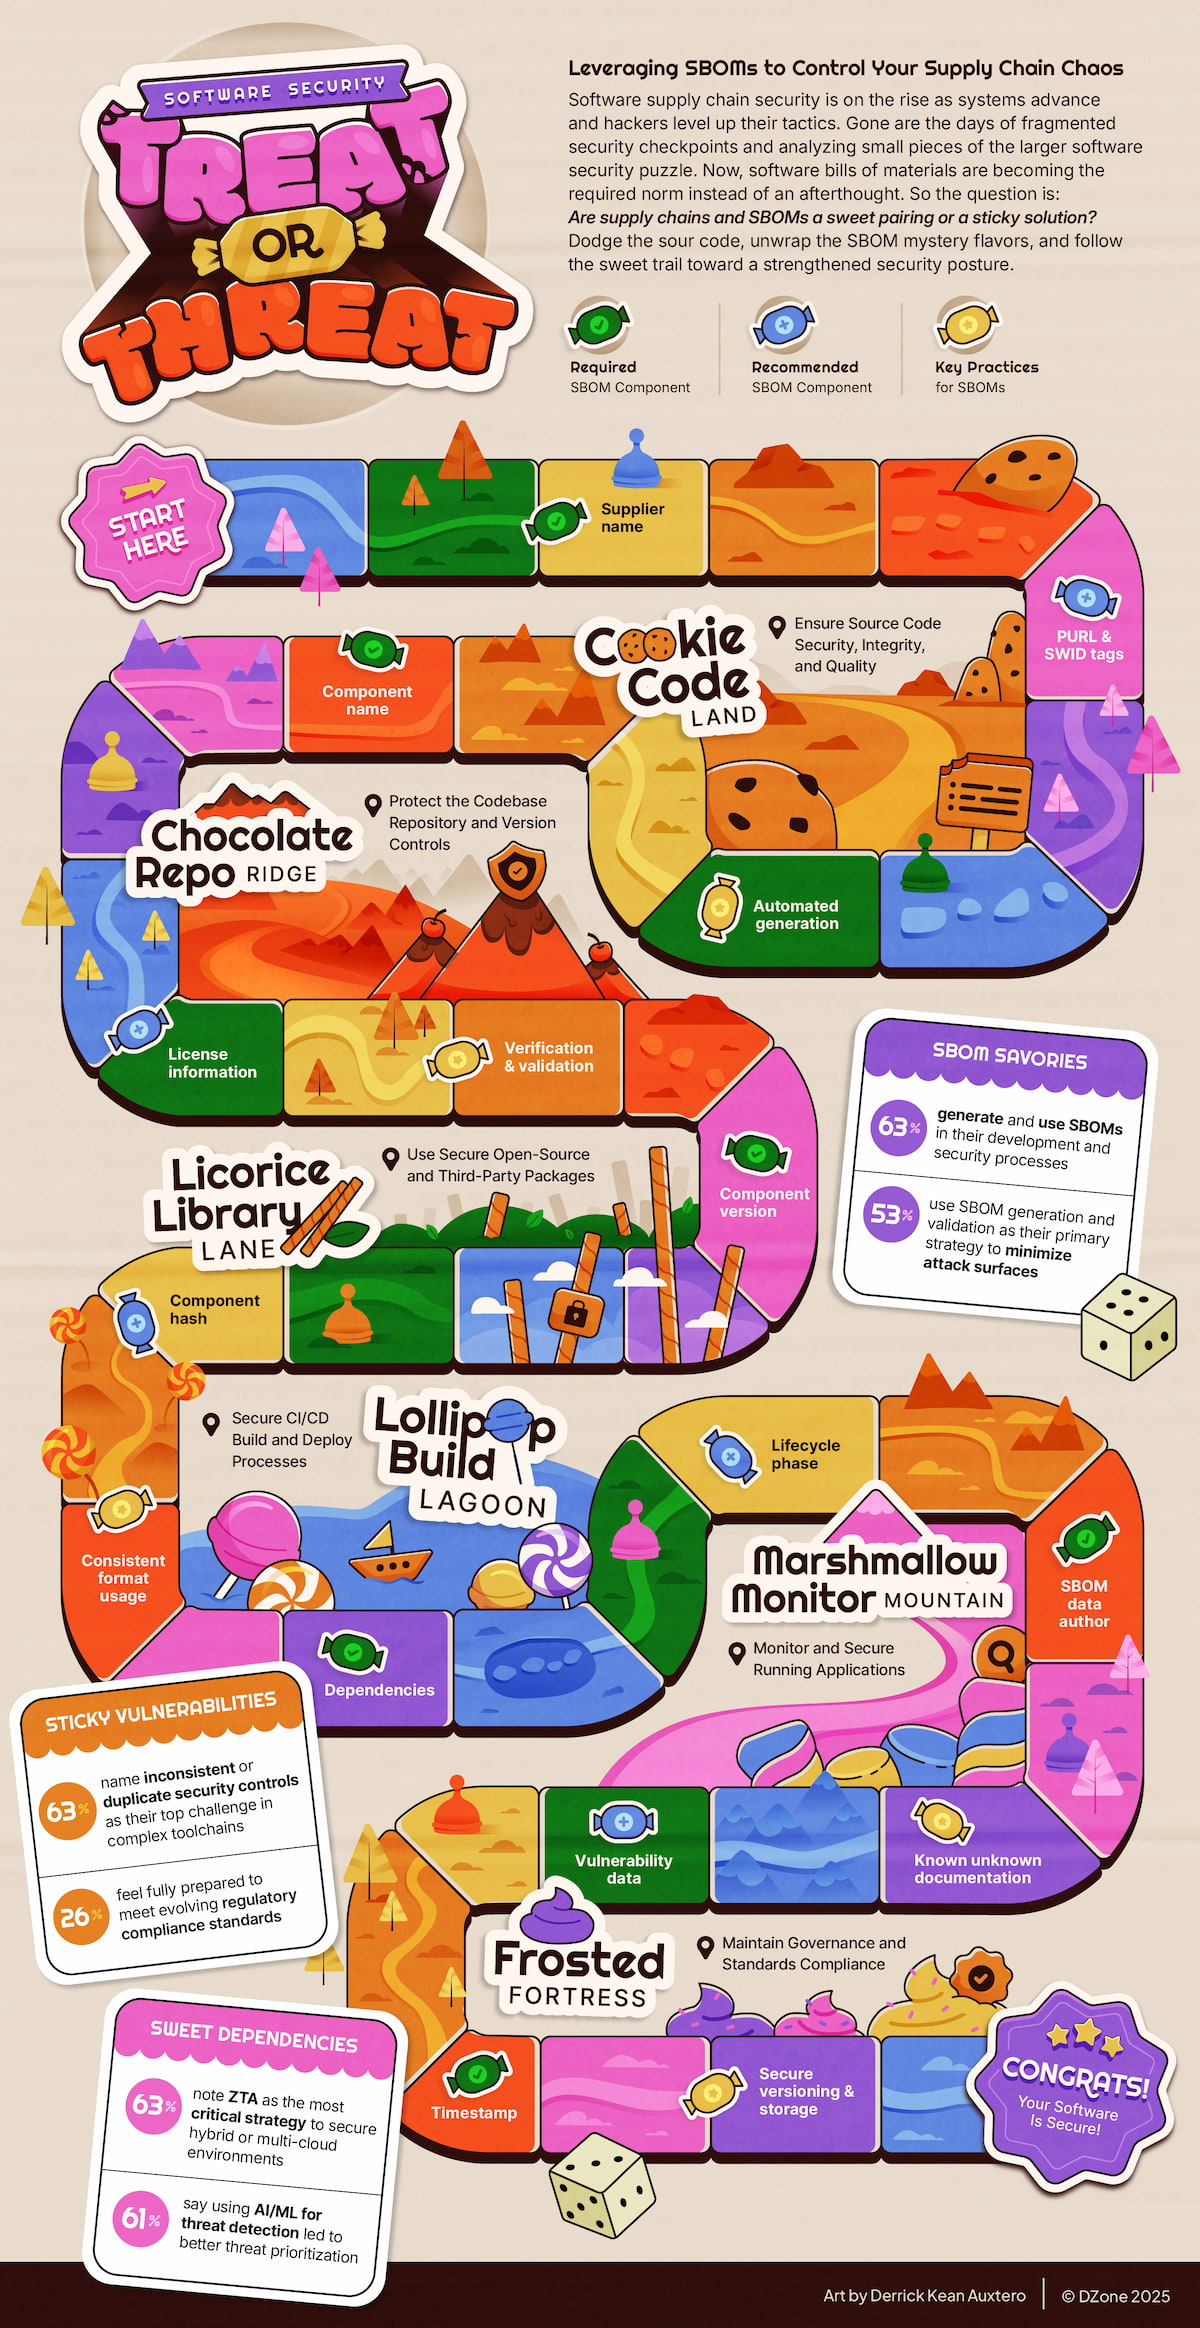

This is an excerpt from DZone's 2025 Trend Report, Software Supply Chain Security: Enhancing Trust and Resilience Across the Software Development Lifecycle.

Read the Free Report

Supply chain management security SBOM

Opinions expressed by DZone contributors are their own.

Related

  • Sharing SBOMs Securely Without Giving Too Much Away
  • Advanced Docker Security: From Supply Chain Transparency to Network Defense
  • How Migrating to Hardened Container Images Strengthens the Secure Software Development Lifecycle
  • Technical Deep Dive: Scaling GenAI-Enhanced SBOM Analysis from Trivy Fix to Enterprise DevSecOps

Partner Resources

×

Comments

Loading comments

The comments didn't load

Please try again in a moment.

Likes

Loading

The next likes didn't load. Please try again.

The likes didn't load

Please try again in a moment.

See who liked this

Log in or join DZone for free to see who liked this article.

Log in Join for free
  • RSS
  • X
  • Facebook

ABOUT US

  • About DZone
  • Support and feedback
  • Community research

ADVERTISE

  • Advertise with DZone

CONTRIBUTE ON DZONE

  • Article Submission Guidelines
  • Become a Contributor
  • Core Program
  • Visit the Writers' Zone

LEGAL

  • Terms of Service
  • Privacy Policy

CONTACT US

  • 3343 Perimeter Hill Drive
  • Suite 215
  • Nashville, TN 37211
  • [email protected]

Let's be friends:

  • RSS
  • X
  • Facebook