

Monitoring journald Logs With Event-Driven Ansible
In this article, see how to monitor journald logs in real time and automate actions using Event-Driven Ansible (EDA).
 CORE
·
Monitoring journald is essential for keeping systems running smoothly and securely. By regularly checking logs generated by systemd, administrators can catch potential issues like failing services or resource constraints — before they turn into major problems. Beyond performance and troubleshooting, journald is a powerful tool for security and compliance. It helps track login attempts, privilege escalations, and unusual service behavior, making it crucial for detecting unauthorized access or potential cyber threats. For organizations that need to meet regulatory requirements, monitoring system logs ensures proper tracking of system changes and security policies.
About the Module
ansible.eda.journald is an Event-Driven Ansible (EDA) plugin that listens to journald logs in real time and triggers automated responses based on log events. This makes it useful for tasks like automatically restarting failed services, detecting security threats, or alerting administrators when critical system issues occur.
Demo
In this article, we explore how the ansible.eda.journald module monitors journald messages and prints debug output whenever a sudo command is issued (condition: match: "_EXE=/usr/bin/sudo"). However, this module can be used to track all journald messages, making it versatile for various logging and monitoring needs.
---
- name: Journald Demo
  hosts: localhost
  sources:
    - name: range
      ansible.eda.journald:
        match: "_EXE=/usr/bin/sudo"
  rules:
    - name: "Print Journald Event message"
      condition: event.journald._comm == 'sudo'
      action:
        print_event:
          pretty: true
          var_root:
            journald.message: journald.message
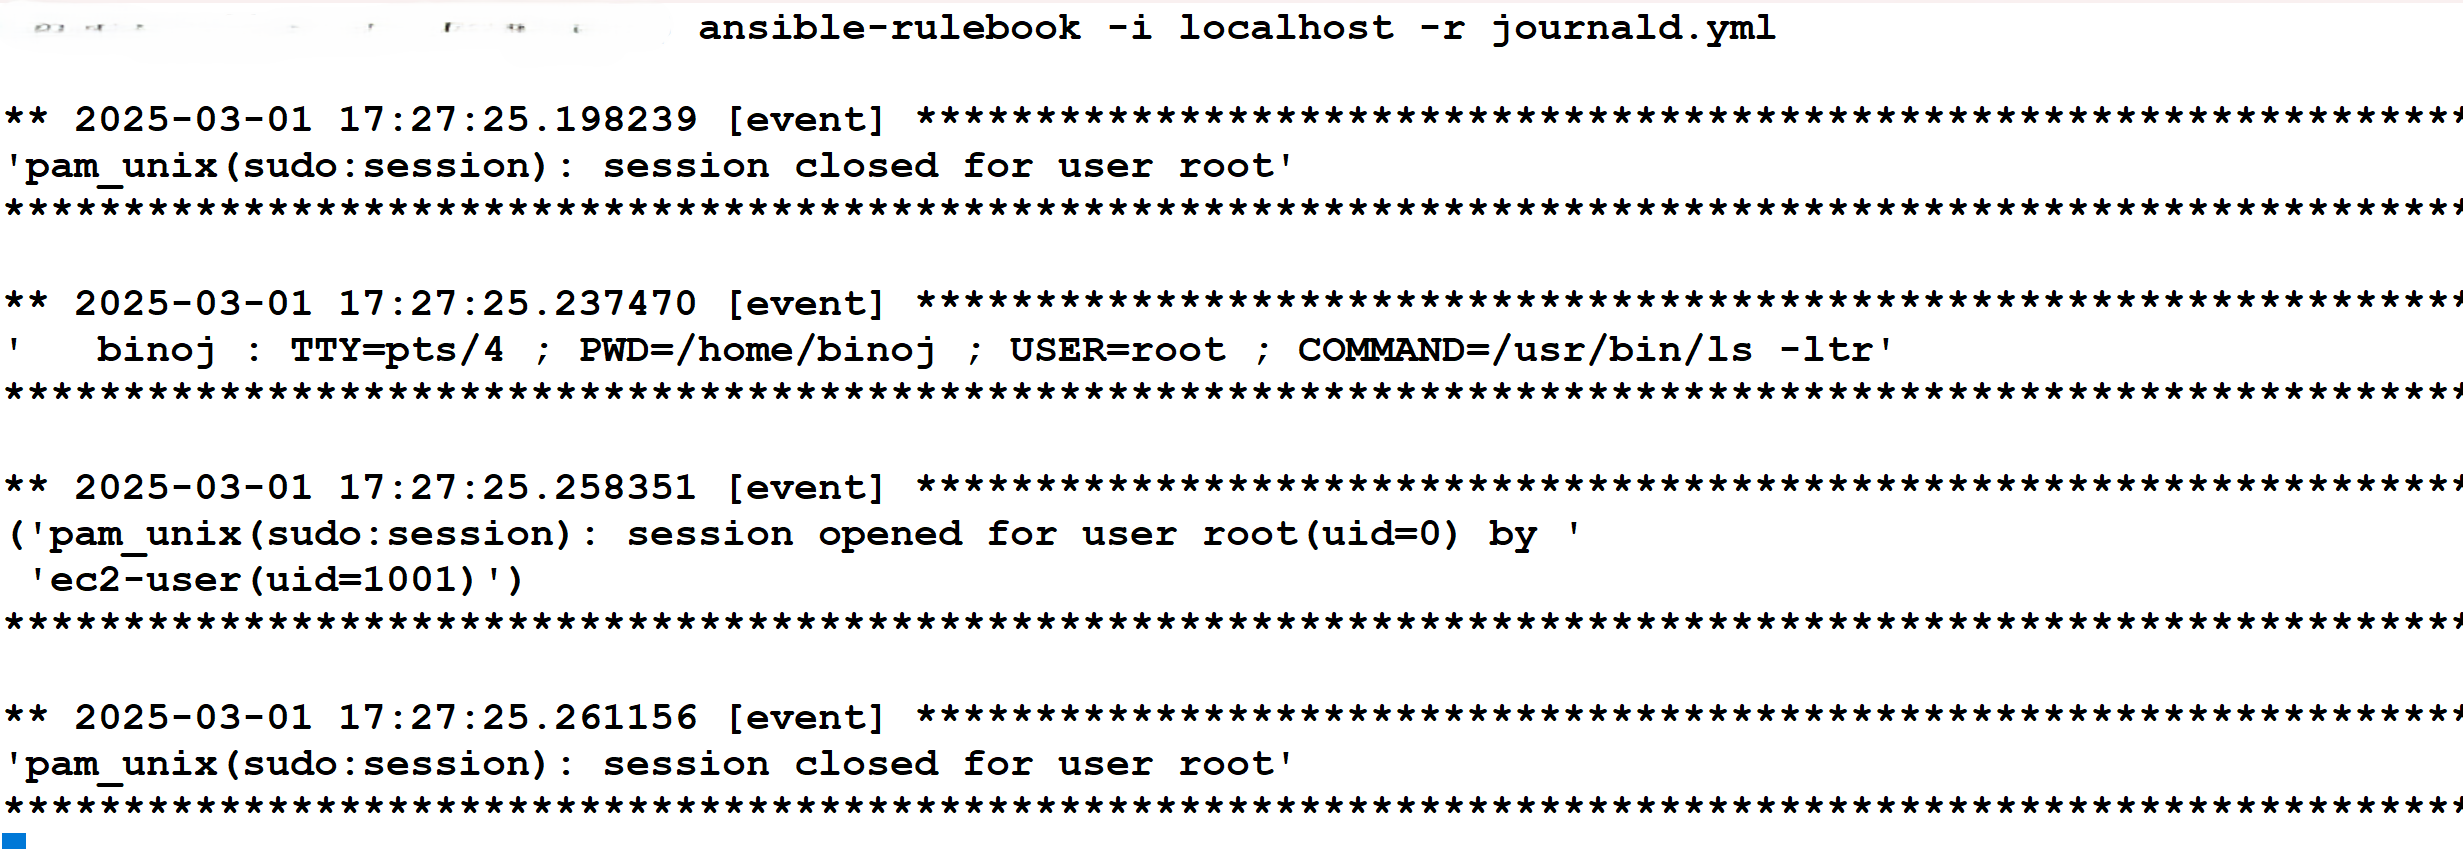
To execute the sample rulebook, run the command, ansible-rulebook -i localhost -r journald.yml, which will start monitoring journald logs in real time. Whenever it detects the use of a sudo command, it will trigger the rule and display a message on the console. This setup provides an easy way to track sudo usage, and you can customize the rulebook to monitor other journald events based on your requirements.
Conclusion
The ansible.eda.journald module provides a powerful way to monitor journald logs in real time and automate responses based on specific events. By leveraging Event-Driven Ansible (EDA), administrators can efficiently track system activities, detect security events, and automate actions such as alerts or service restarts.
This tutorial demonstrated how to set up and run a rulebook to monitor sudo commands, but the same approach can be extended to various other system logs. With its ability to customize rules, ansible.eda.journald is a powerful tool that enhances system monitoring, strengthens security, and automates responses to important events.
Note: The views expressed in this article are my own and do not necessarily reflect the views of my employer.
Opinions expressed by DZone contributors are their own.