

Mule 4 LDAP Operations
Learn how to connect to any LDAP server and perform every LDAP operation.
Lightweight Directory Access Protocol (LDAP) is a client/server protocol used to access and manage directory information. It reads and edits directories over IP networks and runs directly over TCP/IP using simple string formats for data transfer. It was originally developed as a front end to X.500 Directory Access Protocol. Lightweight Directory Access Protocol is also known as RFC 1777.
The LDAP Connector will allow to connect to any LDAP server and perform every LDAP operation. We have implemented a few basic operations in Mule 4.
Search Operation
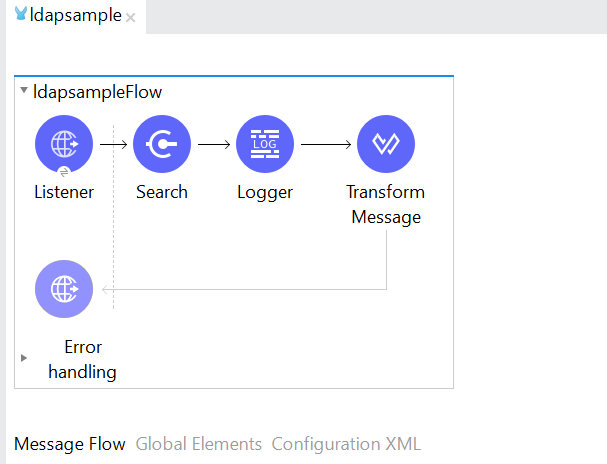
Step1: Create a project in anypoint studio and drag and drop all the required components from mule component palette as shown in below flow.
Mule 4 LDAP operations:
- Search
- Create OU(organizationalUnit)
- Create a user
- Modify
- Delete
Prerequisites:
- Anypoint studio 7
- Java 8
- OpenLDAP, OUD, OID, Microsoft AD.
Acronyms:
DN |
Distinguished Name |
DC |
Domain Component |
CN |
Common Name |
SN |
Sir Name |
OU |
Organizational Unit |
OUD |
Oracle Unified Directory |
OID |
Oracle Internet Directory |
AD |
Active Directory(Microsoft) |
Search Operation
Step1: Create a project in anypoint studio and drag and drop all the required components from the Mule component palette as shown in the below flow.
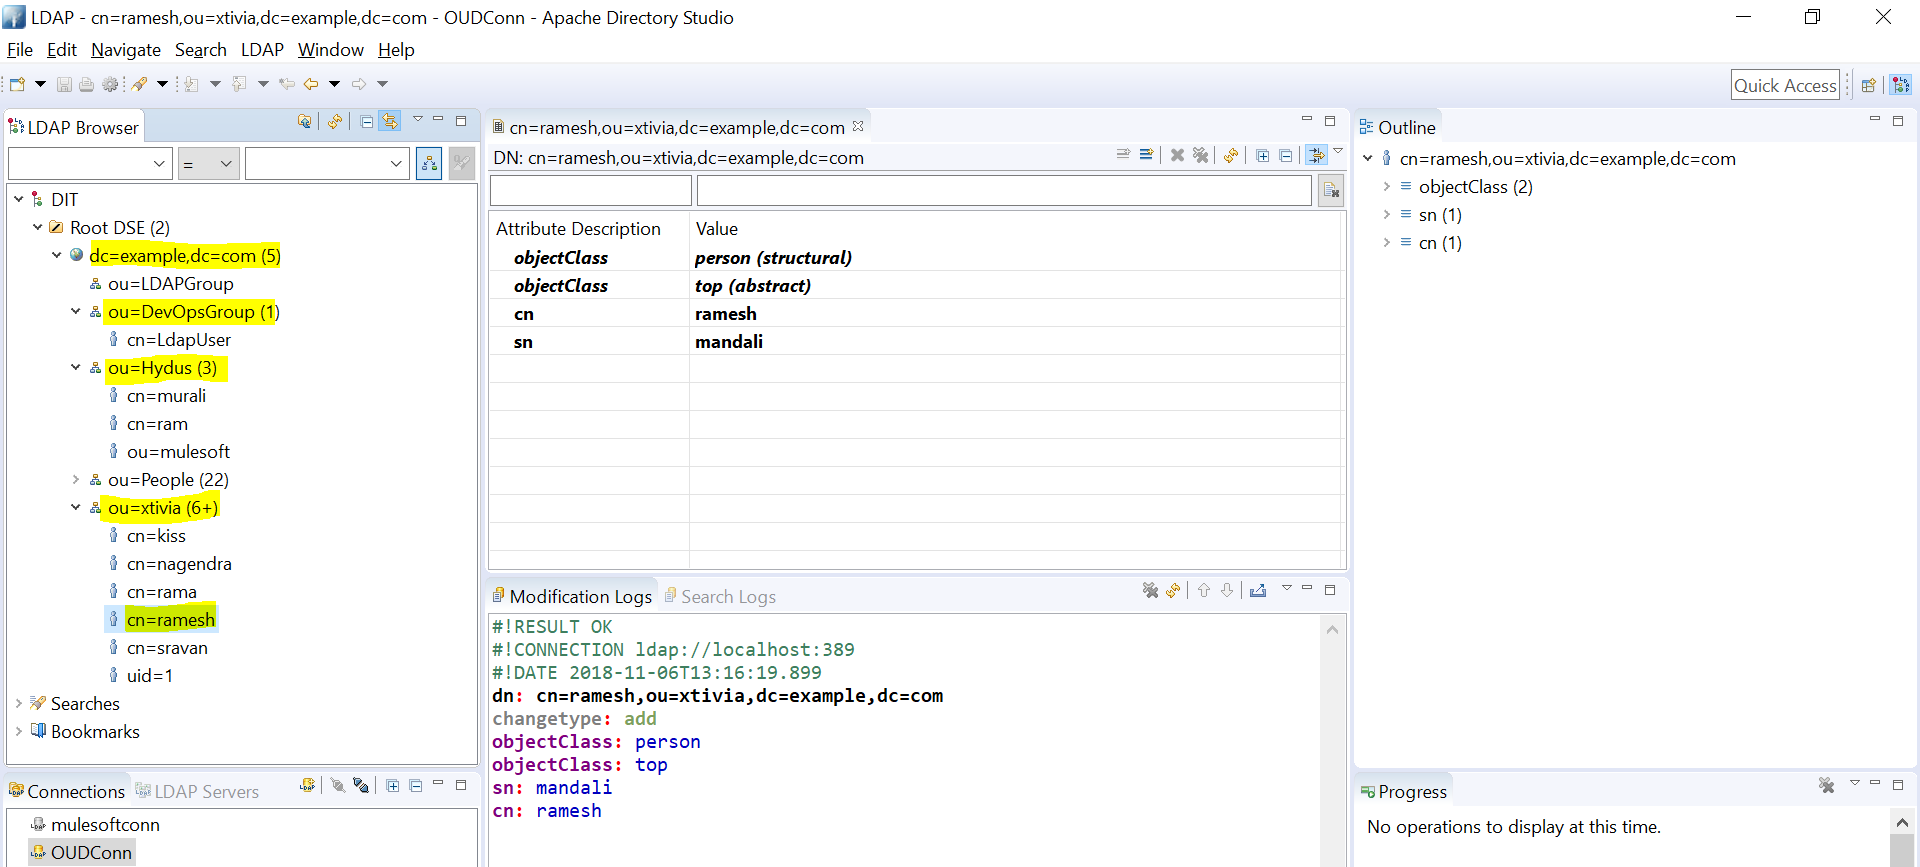
Step2: Install Oracle unified directory LDAP server, as mentioned in the below screenshot. Next, traverse the tree structure of the LDAP server.
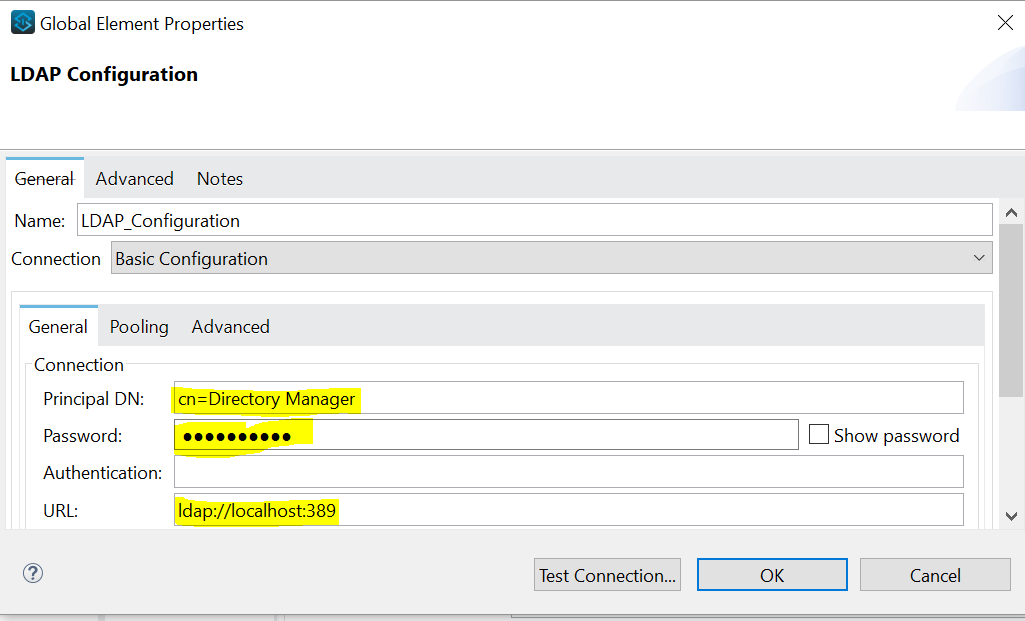
 Step3: In the search component, we must configure LDAP server details.
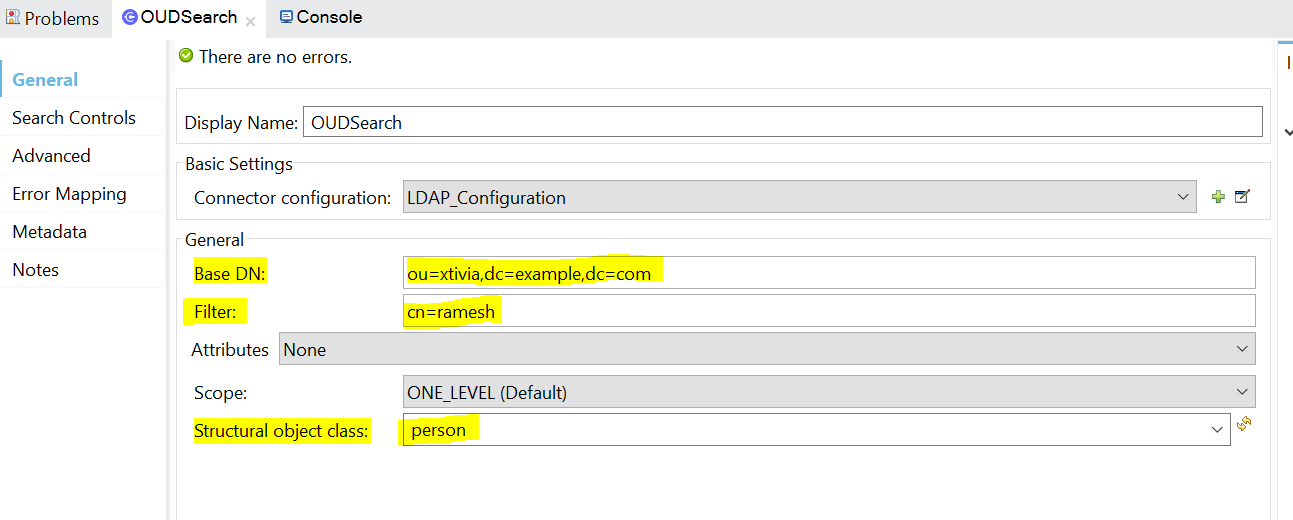
Step4: After configuring LDAP server details, we must provide the Distinguished Name (DN) and filter (should be Common Name (CN)) these are the main fields to search in the LDAP server.
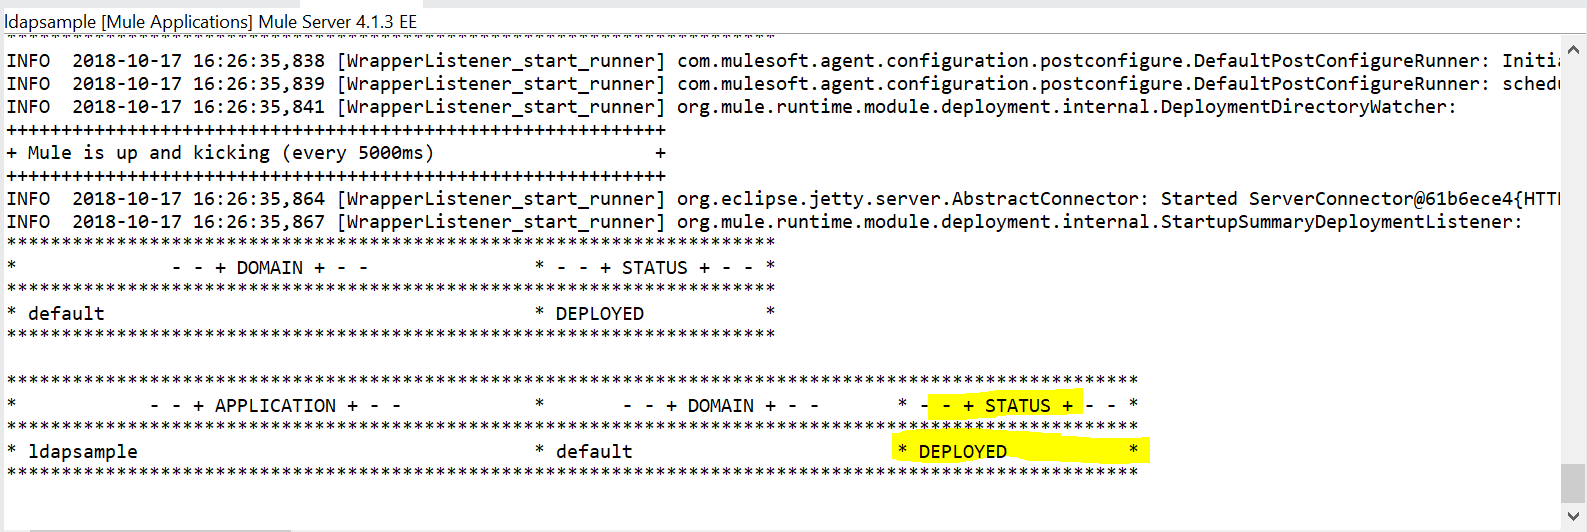
Step5: Once you run the application, it must be deployed status.
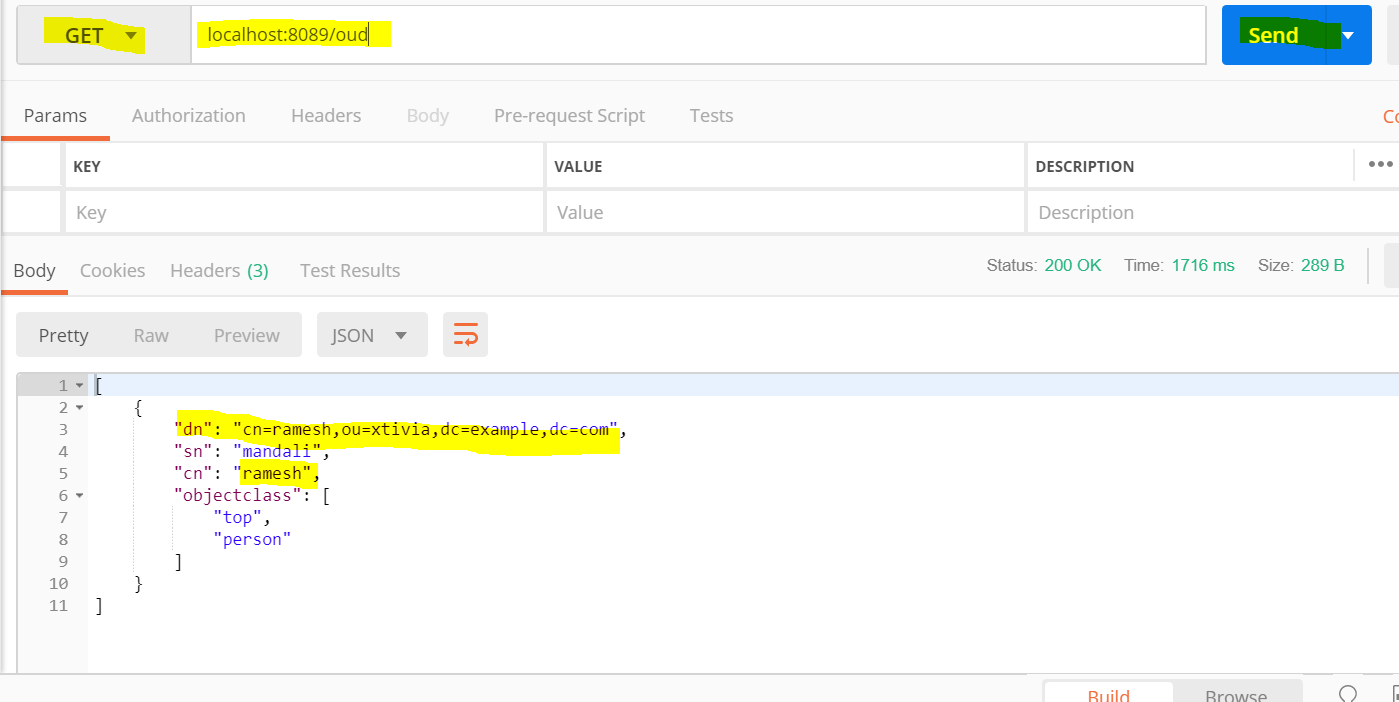
Step6: To test the result, open postman and hit the send button. See the result as below. Common name ramesh has taken as filter so that result given as below. localhost:8089/oud
Create OU (Organizational Unit)
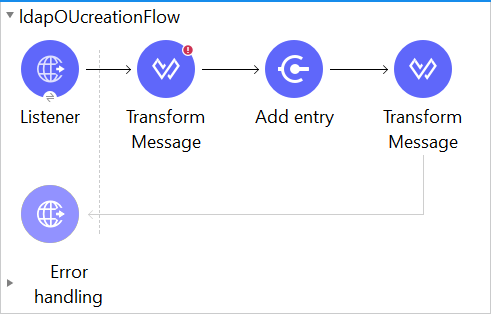
Step1: Create a project in Anypoint studio. Drag and drop all the required components from mule component palette as mentioned in below flow.
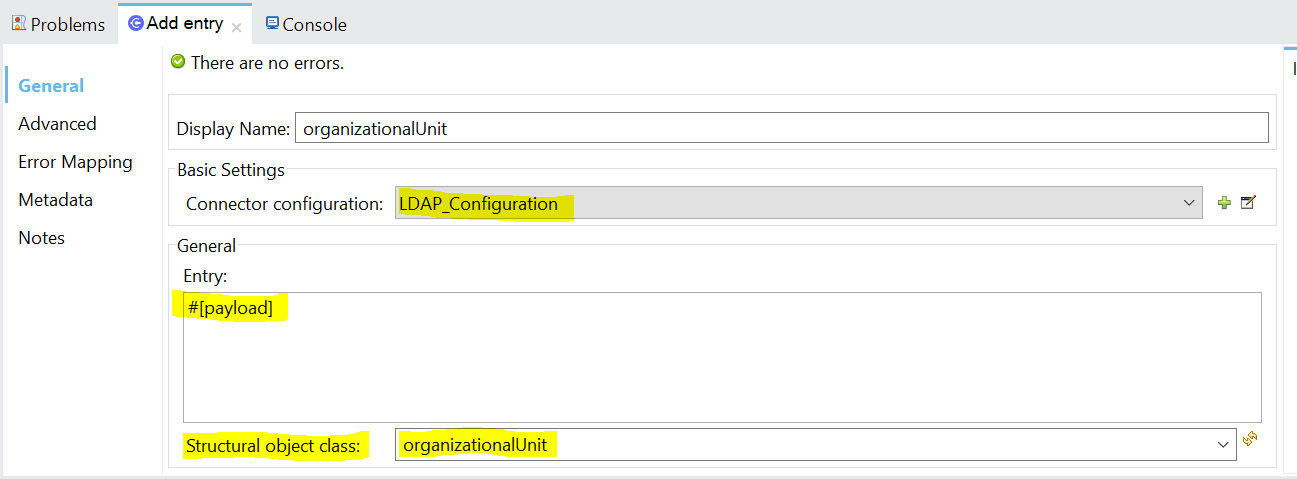
Step2: In add entry component we need to select the structural class as organizationalUnit because I am creating a group on to the LDAP server to create multiple users on this unit.
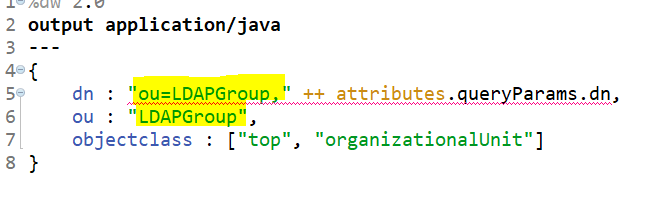
Step3: In dataweave, I am creating a group called DevOpsGroup like organizational Unit (OU). Here, I am getting Distinguished Name(dn) from queryparams.
Top Class: is the super class of all the classes in every LDAP server’s language. if you want to create any user or OU etc…. we must import top class.
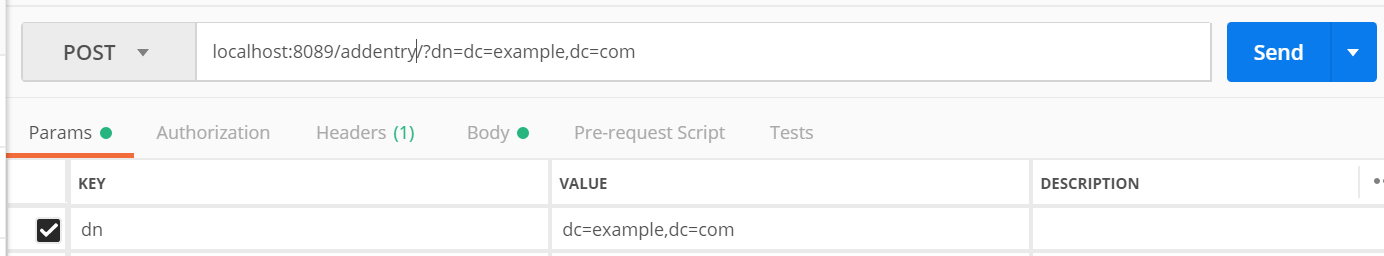
Step4: Once we hit the API from Postman, we can see the logs for add entry operation in the console like below for organizational Unit.
Logs:

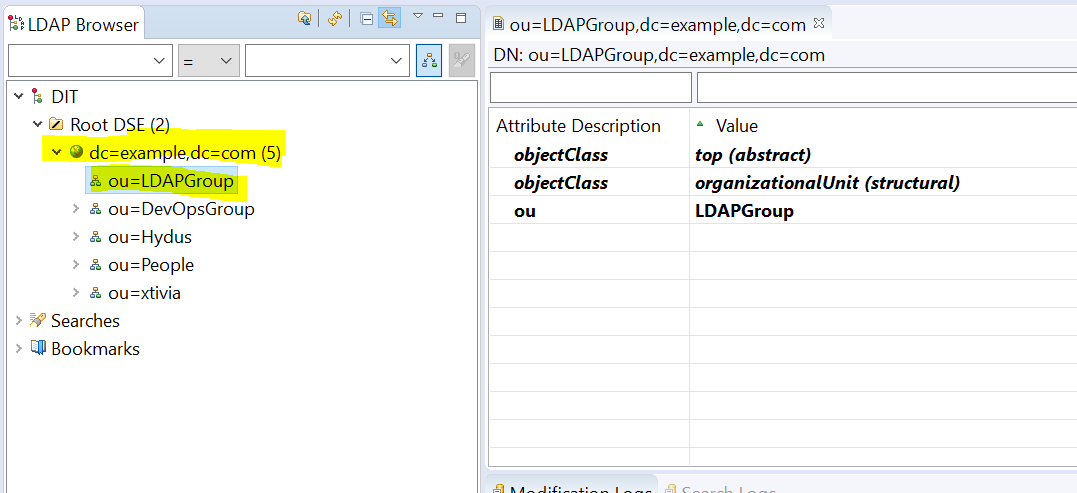
Step5: I have logged into OUD LDAP server and refreshed it to get the updated entry on to the server. Now I can able to see the LDAPGroup OU creation.
Create a user under OU:
Step1: Create a project in Anypoint studio. Drag and drop all the required components from mule component palette as mentioned in below flow.
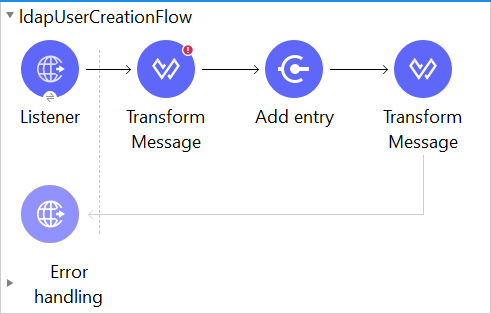
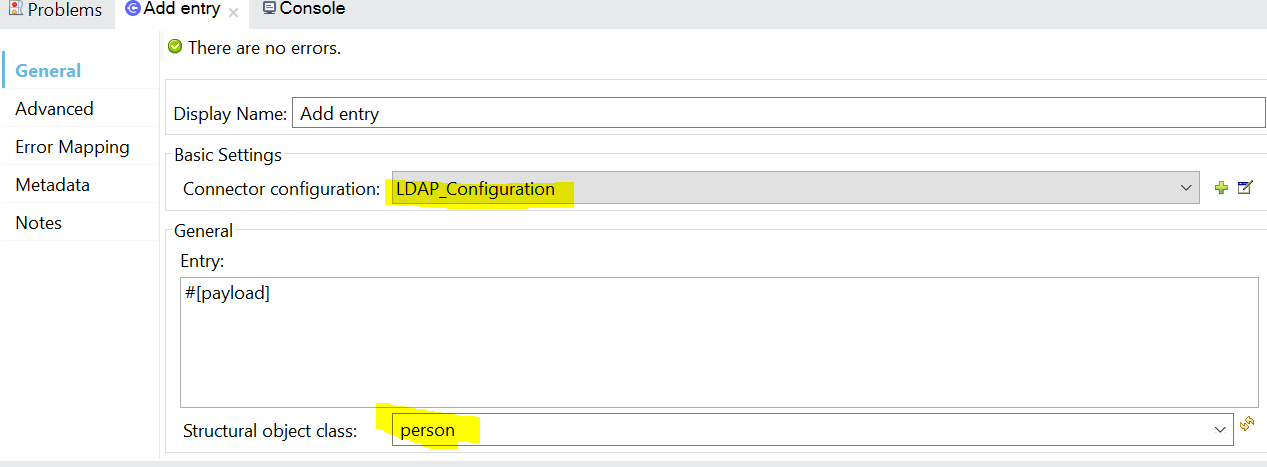
Step2: In add entry component, we need to select the structural class as Person because I am creating a user on to the LDAP server.
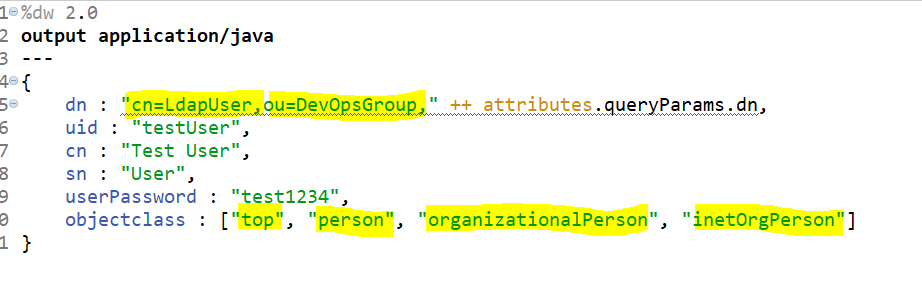
Step3: In dataweave, I am creating a user LdapUser as common name (cn) into DevOpsGroup organizationalUnit(OU). Here I am getting Distinguished Name (dn) from queryparams.
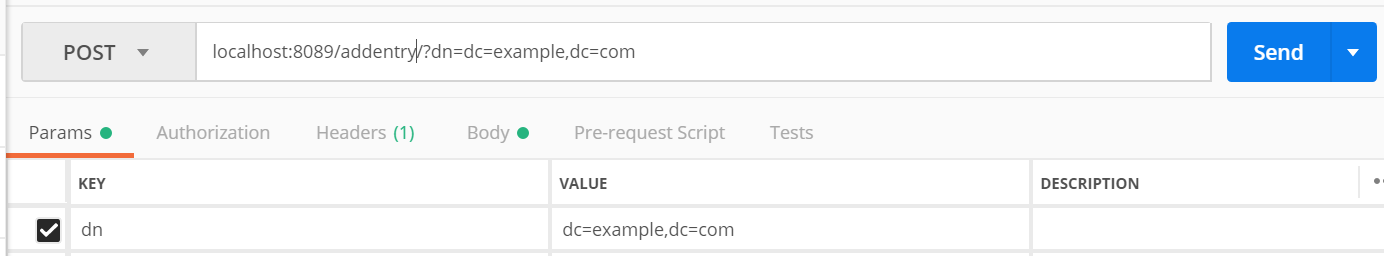
Step4: Once we hit the API from Postman, we can see the logs for add entry operation in the console like below.
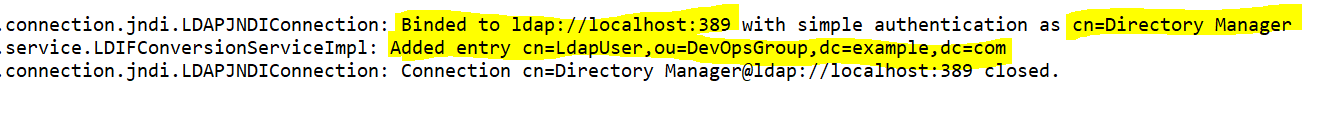
Logs:
Step5: I have logged into OUD LDAP server and refreshed it to get the updated entry on to the server. Now, I am able to see the LdapUser creation.
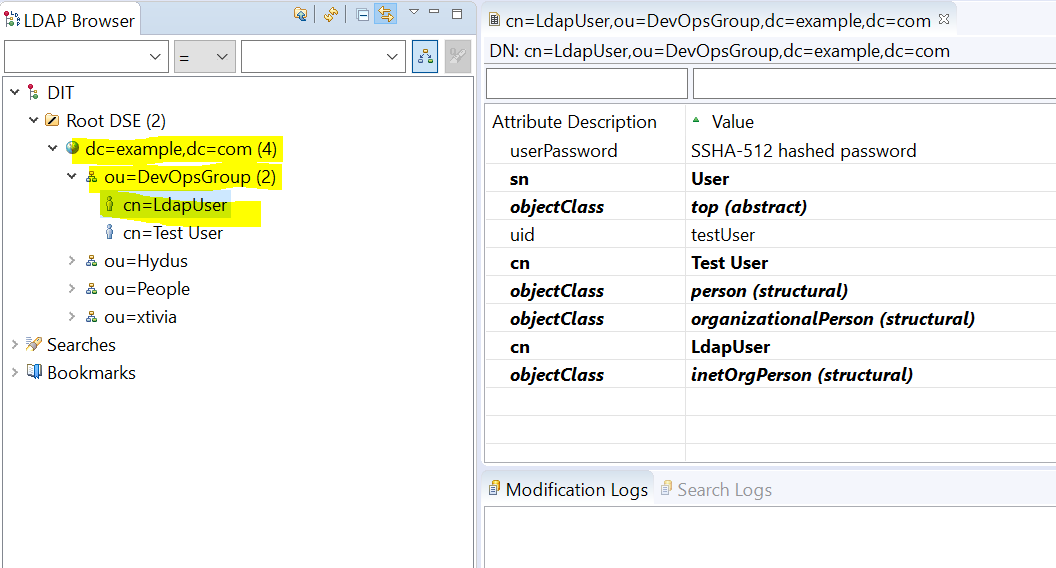
Modify a User:
Step1: Create a project in Anypoint studio. Drag and drop all the required components from the Mule component palette as the below flow shows.
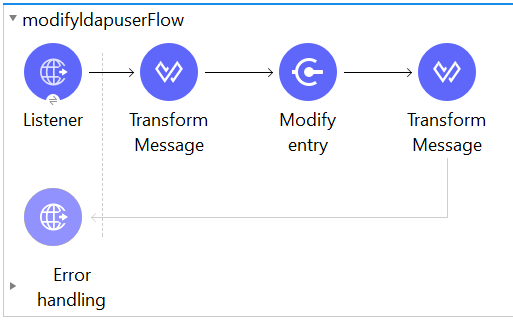
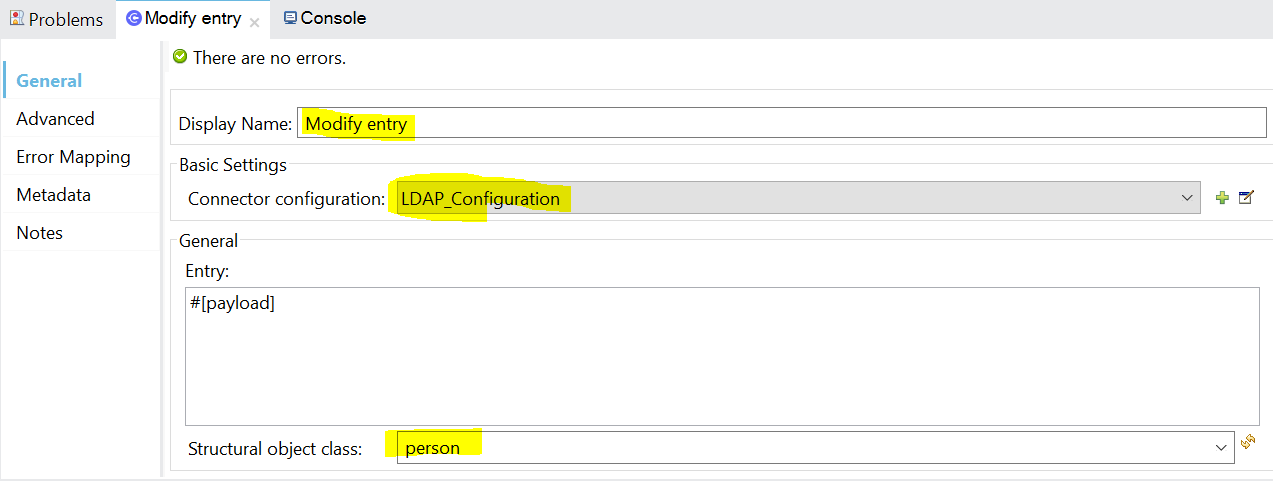
Step2: In the modify entry component, we need to select the structural class as Person because I am modifying a user’s data on to the LDAP server.
Step3: Before modifying the user’s data, the dataweave code needs to be written as mentioned below.
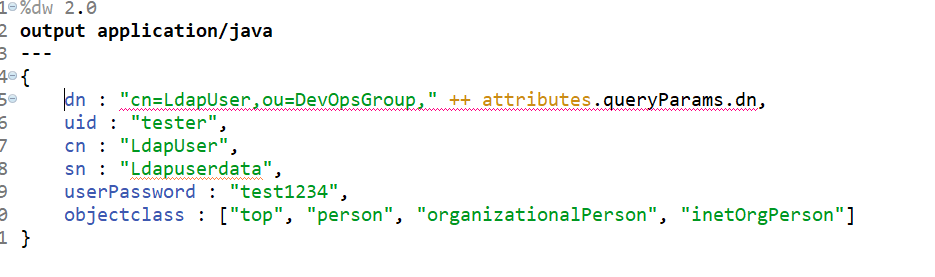
Step4: After the modified user’s data, dataweave should be like below. Here, I am trying to modify LdapUser’s data.
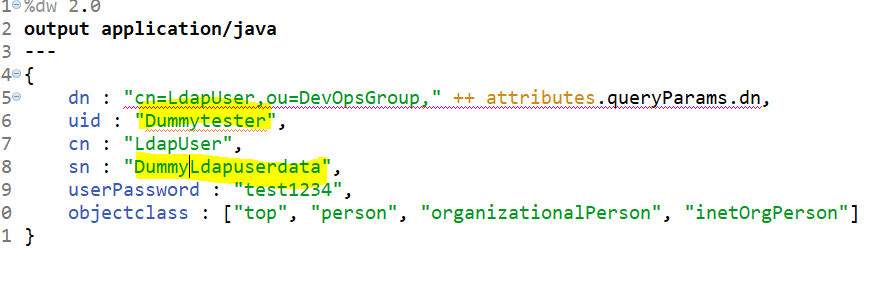
Step5: Once we hit the API from Postman, can see the logs for modified entry data in the console like below.
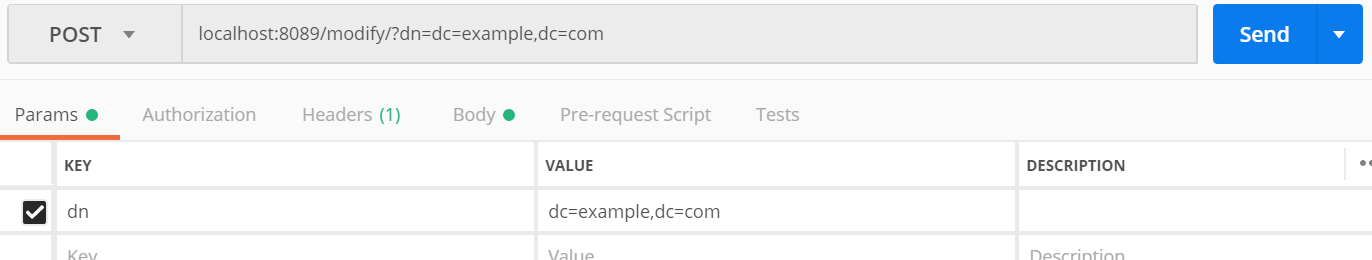
Logs:
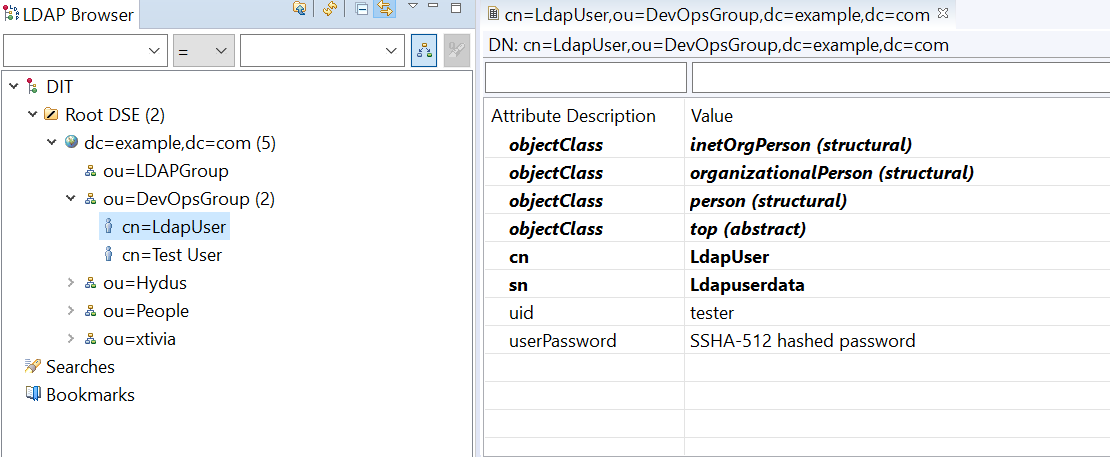
Step5: Before modify user’s data in OUD LDAP server.
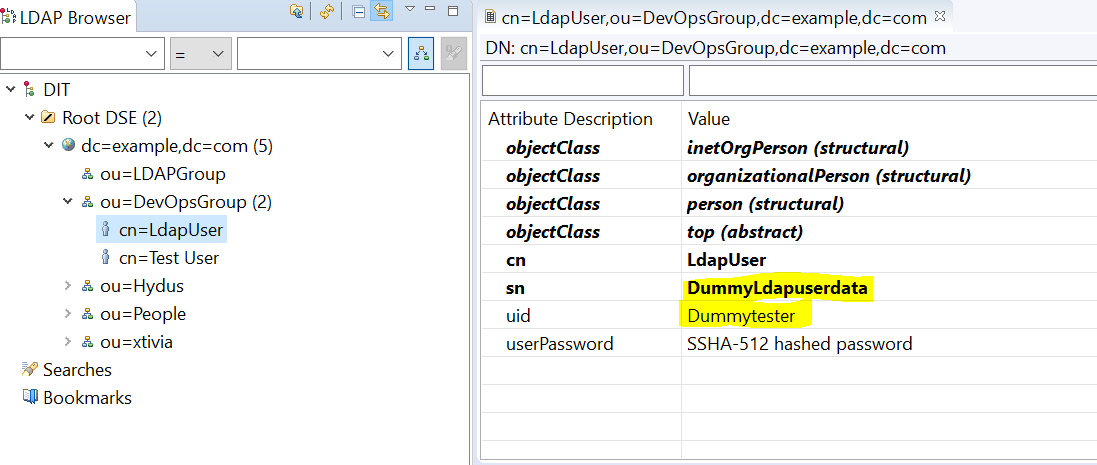
After the modified operation, user’s data is changed as shown below.
Delete operation:
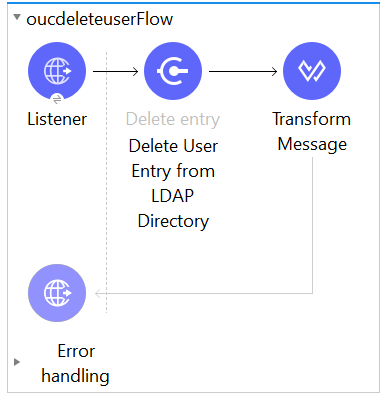
Step1: Create a project in Anypoint studio. Drag and drop all the required components from the Mule component palette as mentioned in the below flow.
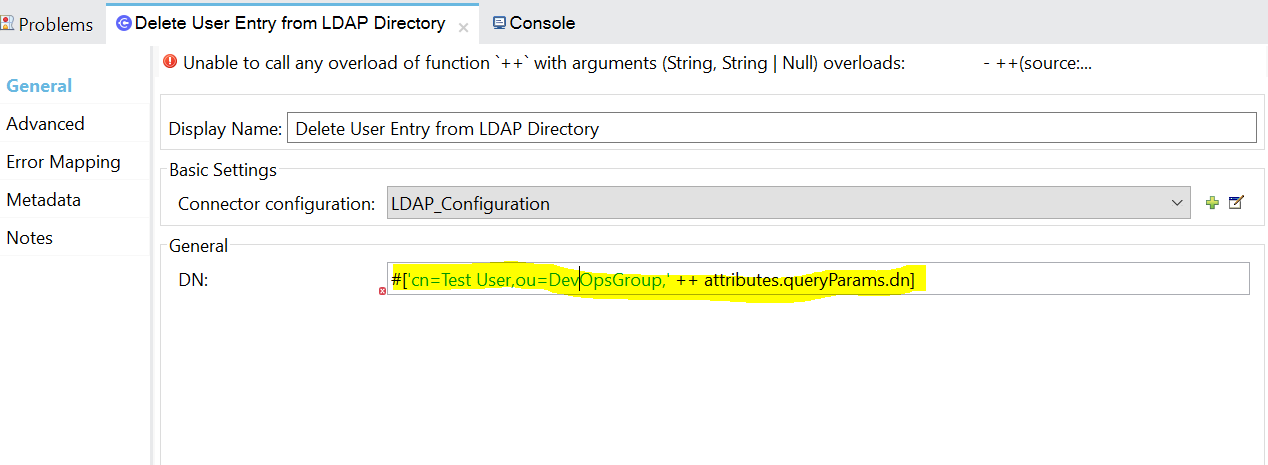
Step2: In the delete component, we must provide the DN. The user will delete based on the DN condition like below.
Step3: Once we hit the API from Postman, we can see the logs for add entry operation in the console like below.

Logs:

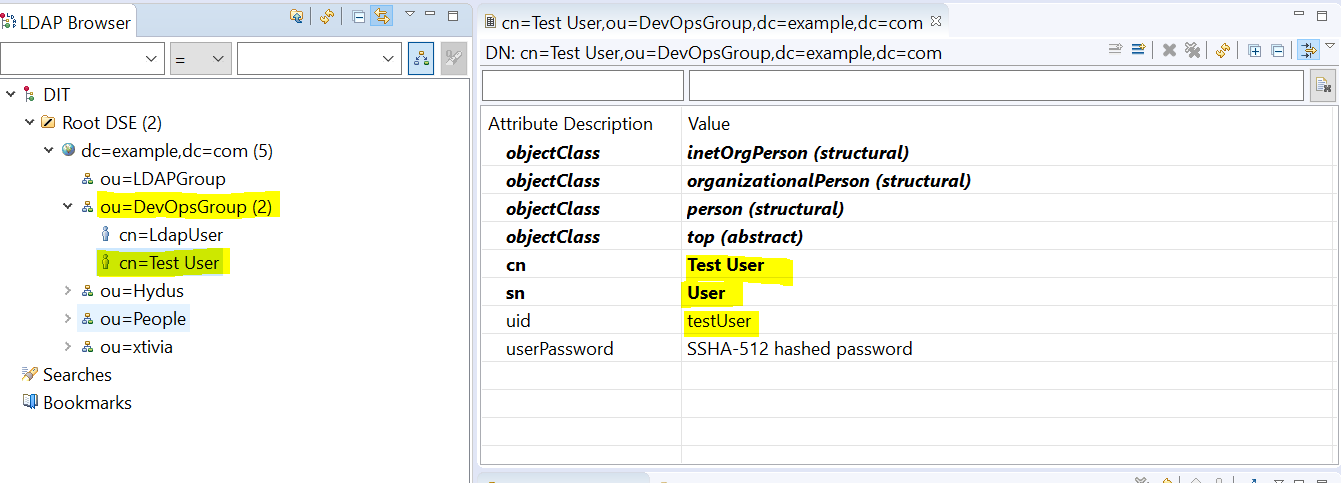
Step4: Before deleting a user on the LDAP server, we can see Test User as mentioned in the below screen.
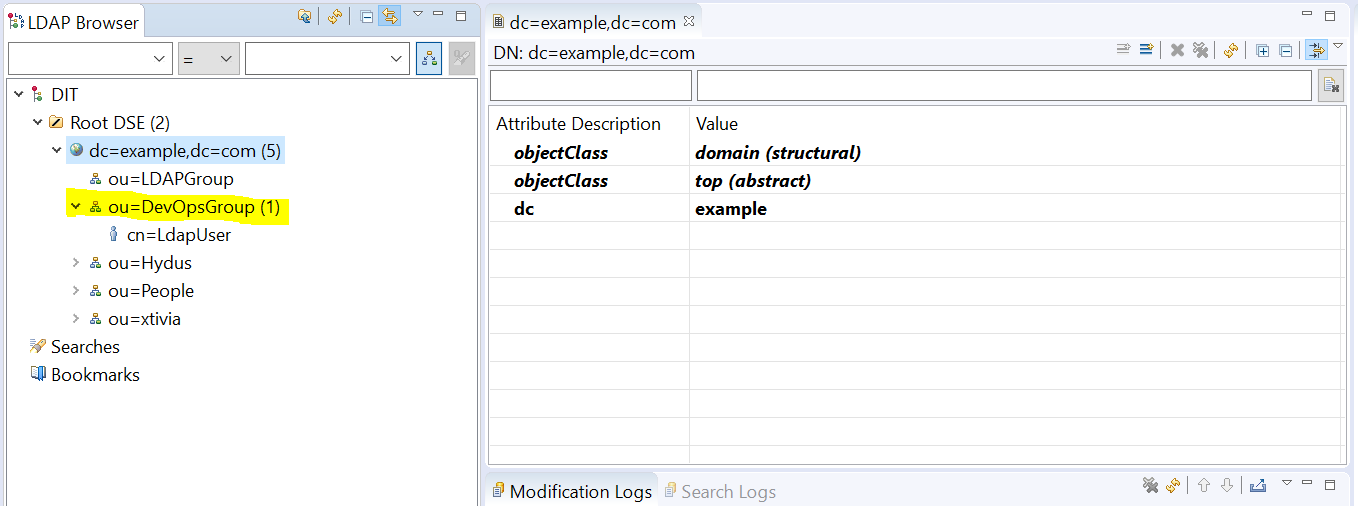
After deleting a user on LDAP server.
Opinions expressed by DZone contributors are their own.